In Washington, recent developments revealed that hackers affiliated with the Chinese state breached various U.S. government computer networks, including major entities like NASA and the U.S. Senate, before federal authorities took action to shut down their related web domains.
The Department of Justice and FBI disclosed on Wednesday the confiscation of three domains tied to the Chinese hacking group QTFY, which were reportedly utilized to infiltrate essential infrastructure and sensitive systems, as detailed in an FBI affidavit.
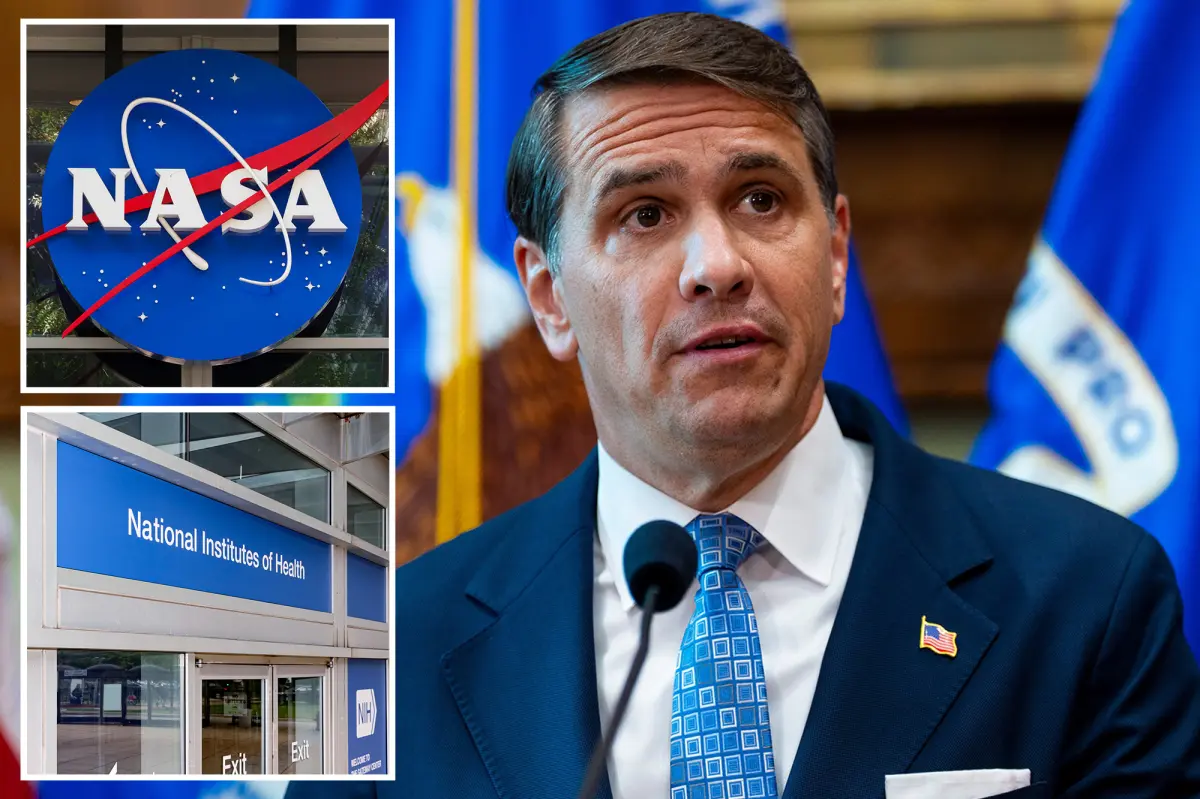
According to the affidavit, since 2018, QTFY has managed to access networks belonging to NASA, NIH, the Department of Justice, the Department of Health and Human Services, three National Laboratories under the Department of Energy, the Federal Reserve, and the Senate.
The affidavit also indicated that these hackers were involved in an international money laundering scheme.
Attorney General Todd Blanche mentioned that the hackers targeted “hospital systems and health care centers,” which is alarming given the current global health crisis.
The newly released information indicates that these infiltrations occurred between 2018 and 2026, although it lacks specifics on what the hackers were actually after or whether they caused any significant damage.
Blanche asserted, “We will stop and prosecute state-sponsored malicious hackers that threaten America’s critical infrastructure. Our commitment is to ensure security for the American people.”
Furthermore, federal law enforcement took action against the malicious software linked to the People’s Republic of China, as part of ongoing efforts to dismantle widespread hacking actions sponsored by the state.
QTFY reportedly sold its hacking capabilities—referred to as “QScan” and “QTRouter”—to entities like the Chinese Ministry of State Security and the People’s Liberation Army through a private firm called Nanjing Xinjiuwei Network Technology Co.
The impact was significant, as the systems were capable of compromising thousands of devices worldwide. The affidavit highlighted specific targets, including a medical center in Ohio and financial institutions in Michigan and South Korea.
FBI Director Kash Patel communicated in a statement, “Today, we revealed the disruption of a global botnet and hacking framework being utilized by Chinese state-sponsored hackers against U.S. critical infrastructure.”
Further commenting on the matter, Patel noted that these tools helped the hackers obscure the origins of their attacks, emphasizing the collaborative effort between the FBI Cyber Division and DOJ partners that enabled the seizure of adversary infrastructure.
Patel concluded with a reminder that this is part of an ongoing strategy against PRC-sponsored hacking, aligning with President Trump’s directive for cybersecurity, underscoring the FBI’s enhanced focus on defending against cyber threats to the nation.