Homeland Security data leak exposes records tied to more than 41,000 workers
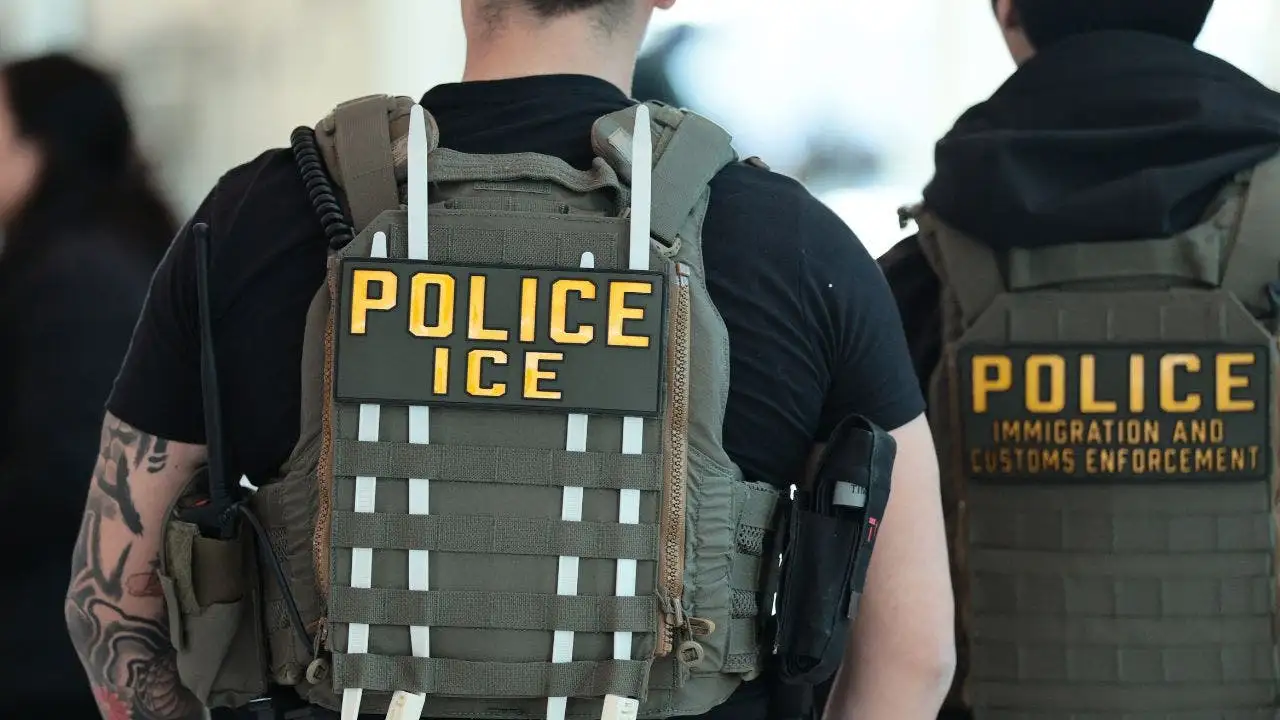
A leaked collection of Homeland Security records has exposed information about more than 41,000 employees and contractors, including staff connected to sensitive operations. The files reportedly include work contact details, office locations and internal access groups. Some of those groups reference surveillance programs and artificial intelligence tools used across the department.
Federal officials are investigating the breach as concerns grow about possible risks to agents and their families. The incident also shows how ordinary workplace information can become more dangerous when it is gathered in one place and made public.
On Oct. 28, the nonprofit Distributed Denial of Secrets published a collection of records called Icepick. The files reportedly came from a group calling itself the Department of Peace, which says it gained access to government systems. The collection covers the Department of Homeland Security and seven agencies within it, including Immigration and Customs Enforcement and Customs and Border Protection.
The records include employee names, agency email addresses, work locations and phone numbers, some identified as mobile numbers. They also list supervisors and internal access groups. It has not been established that private home addresses were included.
More than half the records are associated with Customs and Border Protection. About 10,000 relate to ICE, and roughly 6,200 to U.S. Citizenship and Immigration Services. The records were last updated Aug. 19, meaning some employees may since have moved to different roles. Even so, the collection offers a substantial amount of detail about how parts of the department are organized.
Some of the most concerning entries point to internal groups associated with undercover investigations. WIRED identified 39 Homeland Security Investigations employees linked to groups referencing certified undercover operations. Other group names refer to communications interception programs and surveillance tools. The files also show reporting relationships that could help outsiders piece together how different teams work.
That information could put ongoing investigations at risk, though membership in an access group does not by itself prove that someone was working undercover. The records offer indications of sensitive assignments, not a complete picture of each employee’s duties. Former acting ICE director John Sandweg described the exposure as a “nightmare scenario,” warning that it could endanger agents and disrupt criminal investigations.
The files also name technology used within the department. Some access groups refer to Palantir’s Falcon investigative platform and software related to surveillance and phone-record analysis. Other groups mention ChatGPT, Google Gemini and Microsoft Copilot. One group named “Grok.com” included eight DHS technology officials.
Those references do not establish that employees used the services, or that any of the technology companies were breached. Group names can reflect permissions rather than actual use. Still, the records give outsiders a glimpse of tools and systems available to some personnel at an agency responsible for national security.
The group claiming responsibility says it obtained the information through DHS’s Okta sign-in system. Okta, which provides identity and access-management services, says it has no evidence its own systems or data were compromised. The route by which the records were accessed remains unclear.
DHS has acknowledged a potential breach and says it is investigating. The department has not confirmed how the information was obtained. So far, public reporting has focused on personnel details and access-group information; it has not confirmed that passwords, intercepted communications or investigative case files were exposed. Without more information, it would be premature to attribute the incident to a particular vulnerability or software provider.
A DHS spokesperson said the department was working to address the situation and took threats to employees and officers seriously. The department said it would share further information when available.
As the records circulated online, DHS tried to restrict access. On Oct. 29, a company reportedly authorized to request content removals on ICE’s behalf contacted Icelandic hosting provider FlokiNET. The request said the database exposed more than 40,000 identifiable people to possible harassment and physical harm. FlokiNET declined to remove the material, saying it contained workplace contact information rather than private home details.
The database was briefly unavailable before appearing elsewhere. On Oct. 30, SITE Intelligence Group reportedly identified threatening online comments following the release, including threats aimed at immigration officers and their families. Even if original files are taken down, copies may continue to circulate.
Workplace details can also help criminals make scams more convincing. A message from someone claiming to be an employer’s IT staff may seem credible if it includes a supervisor’s name, a work email address or a reference to an internal system. Attackers can combine leaked information with details found elsewhere to impersonate colleagues or tailor phishing attempts.
People may have little control over how their employers store personnel records, but a few habits can make targeted scams harder. If someone contacts you claiming to work in IT, verify the request through a phone number or channel you already trust. Be wary of unexpected password-reset messages, especially if they pressure you to act quickly, and avoid signing in through links in those messages.
Use unique passwords for important accounts and turn on multifactor authentication or passkeys where possible. Your main email account is particularly important because it may be used to reset access to other services. Check that the recovery phone number and email address on your accounts have not been changed without your knowledge.
It may also be worth searching your name online and reviewing what information is publicly visible. Old work profiles, social media accounts and people-search sites can reveal more than you expect. Data removal services may help get information taken down from some broker websites, but they cannot guarantee removal everywhere or erase copies of a leak. Reviewing privacy settings and limiting public details about your home or daily routine can help reduce exposure.
The reported DHS records have not been confirmed to include Social Security numbers or financial account details. Still, exposed contact information can support convincing impersonation attempts. Watch for unfamiliar account activity and suspicious reset notices. If you believe sensitive identity details have been exposed, consider contacting the major credit bureaus about placing a credit freeze.
If someone uses workplace information to impersonate a colleague or makes threats, save messages and screenshots and report the incident to your employer’s security team. Threats of violence should be reported to law enforcement. Employees who think their information may be involved can ask their employer what was exposed and what precautions are recommended. Be cautious of unsolicited callers who claim they can confirm your involvement.
The leak highlights an uncomfortable tension. The public has a legitimate interest in how federal agencies operate and how officers are held accountable. At the same time, making information about personnel in sensitive roles searchable could endanger employees, their families and active investigations. DHS will need to explain how the records were exposed and what it is doing to prevent a similar incident.