Technology outages that affected banks, air travel and even the National Security Agency have highlighted how vulnerable essential systems could be during a conflict, national security experts say. The disruptions have fueled questions about whether the incidents were connected, but Trump administration officials have said they were not the result of a coordinated cyberattack.
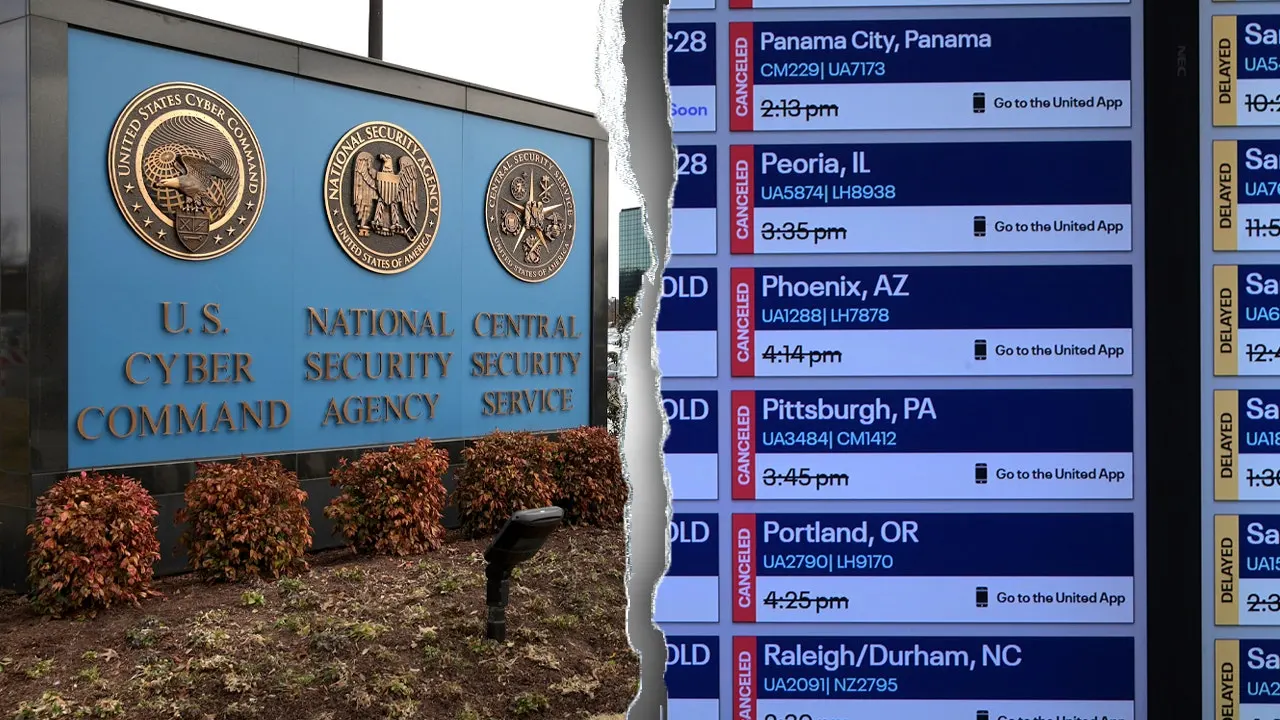
Over six days, technical problems affected Microsoft 365, commercial flights, payroll and human resources software, banking transactions and the NSA’s classified internal communications network. Some disruptions had broad consequences: U.S. flights were grounded nationwide for only the second time since the September 11, 2001, attacks.
“This is not a cyberattack, and this is not a coordinated effort by a nation-state,” Director of National Intelligence Jay Clayton said Tuesday.
Homeland Security Secretary Markwayne Mullin also said the outages had nothing to do with cyberattacks. He suggested that technical problems may become more frequent as new technologies are introduced. A day earlier, Mullin had sought to reassure the public, saying the country and its banking system were secure.
The outage at the NSA has drawn particular attention. Its highly classified internal communications network, known as NSA Net, went offline Tuesday, preventing employees from sharing classified information internally. Attendance at the agency’s Fort Meade, Maryland, campus was staggered during the week to reduce demand on systems. The network was restored Friday.
National security and cybersecurity expert Steve Bucci said the disruption stood out because the NSA’s systems, especially its classified networks, are generally separate from those used by other organizations. Its timing alongside the other outages, he said, made it harder to dismiss as coincidence.
A U.S. official said routine maintenance caused the problem. The NSA experienced temporary interruptions to some internal systems, the official said, but its critical operations and national security capabilities remained functional.
Tommy Waller, a national security expert with the Center for Security Policy, said the NSA outage may have resulted from efforts to patch vulnerabilities. Still, he questioned whether the wider pattern was coincidental, pointing to the scale and duration of the disruptions and the range of infrastructure affected.
Former CIA station chief Daniel Hoffman said banks, technology companies and other institutions affected by the outages are frequent targets for foreign governments and cybercriminals. China, Russia, North Korea and Iran, as well as criminal hackers, seek to compromise major organizations, he said, adding that individuals are also potential targets.
The threats are not hypothetical. In July, hackers targeted more than 30 municipal water systems in Minnesota. The incidents were part of a wider series of intrusions across several states, forcing some utilities to operate manually and disrupting water service. Federal investigators considered possible Iranian involvement, but the attacks were not definitively attributed.
The Pentagon is also preparing for the possibility that infrastructure could fail during a major conflict. Under its FORTRESS initiative, military bases in the continental United States are being directed to prepare to maintain essential operations for at least 90 days without outside support, according to previously reviewed documents.
Pentagon spokesperson Sean Parnell has said the military cannot depend on civilian municipal infrastructure to support national defense, describing that reliance as an unacceptable risk.
Waller cited Chinese military writings that discuss attacking civilian communications and infrastructure during a conflict. He stressed that he was not accusing China of causing the recent outages, but said the possibility should be taken seriously because such tactics appear in Chinese military doctrine.
U.S. intelligence and law enforcement agencies warned in 2024 that Chinese state-backed hackers known as Volt Typhoon had infiltrated American communications, energy, transportation and water systems. The group may have positioned itself to disrupt critical services in the event of a conflict with the United States.
Research published last month found that the group continued targeting government, defense and critical infrastructure networks through a separate operation, despite U.S. efforts to dismantle parts of its infrastructure.
Bucci cautioned that a foreign adversary trying to compromise U.S. infrastructure might avoid causing conspicuous failures, since those could alert the targets. An attacker might instead place tools or other access for later use, he said, rather than deliberately making systems malfunction.
The outages have also prompted calls for federal agencies and private companies to be more forthcoming. Hoffman said public confidence in banks and other essential services depends in part on people understanding what has happened. Waller likewise urged officials to be transparent about vulnerabilities and how they are being addressed.