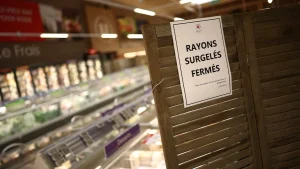
The recent cyberattack that impacted French supermarkets, leading to significant losses, serves as a serious warning for businesses in the U.S., according to cybersecurity specialists. Unknown hackers took control of refrigeration systems in various supermarkets across France, causing temperatures to exceed 100 degrees Fahrenheit overnight and resulting in a vast amount of spoiled goods. John Walsh, a senior vice president at the software company IGEL in Germany, emphasized that this threat isn’t limited to grocery stores—many businesses need to remain vigilant.
Walsh noted, “Imagine if we didn’t have water for a whole week, or if freezers were compromised and food became scarce. It could lead to a tough situation, potentially sparking economic and social unrest.” His role at IGEL involves collaborating with organizations involved in critical infrastructure, such as Siemens and Rockwell, to enhance security measures.
In France, the issue was exacerbated by many affected refrigerators being outdated systems lacking necessary updates, raising concerns about the state of similar infrastructure in the U.S. Walsh pointed out that a significant amount of the nation’s crucial infrastructure is, indeed, overdue for upgrades.
“A major challenge in operational technology environments—whether it’s in food production, pharmaceuticals, or utilities—is that many facilities are still running on assets that are 15 to 20 years old,” he remarked, highlighting that these systems are not only costly but also very delicate and integral to operations.
While working with various decision-makers, Walsh observed a tendency to avoid taking key systems offline for upgrades, operating instead under the “if it’s not broken, don’t fix it” philosophy. However, as technology becomes increasingly intertwined with critical infrastructure, cybersecurity firms are being compelled to adapt their strategies.
“Shifting from a preventive security mindset to one focused on resilience is imperative,” Walsh stated. With hackers using AI to become more sophisticated, simply trying to block them from entering key systems may no longer be effective. Instead, system operators should work under the assumption that hackers may already be present.
Walsh explained that true security is about confidence in the protection measures, while resilience assumes an attacker’s presence and aims to contain potential damage. There could even be a Trojan horse sitting within vital U.S. infrastructure right now, just waiting to be activated.
Previous incidents have shown the capability of malicious actors to disrupt systems, which could be viewed as practice for larger, more coordinated attacks. Policy experts are struggling to find ways to advise lawmakers, especially as so many aspects of everyday life are now internet-connected.
Amy Kremer, chair of Humans First, expressed her astonishment that household appliances can connect to the internet. “While the convenience is appreciated, it also poses significant risks. This should be a concern for all Americans, not just regarding appliances but smart home devices that could be hacked,” she said. She added, “Technology has revolutionized the world, yet with that advances vulnerabilities have emerged.”
Walsh stressed that the U.S. infrastructure is indeed susceptible to such threats, recalling the coordinated cyberattack on Minnesota’s water systems in 2026 as a prime example. “If one were to attempt to disrupt the U.S. economy or conduct acts of terrorism, targeting water and food supplies would be the strategy—just like what we’ve seen recently,” he noted.
He concluded with a call to action: strengthening governance measures for industries, urging that citizens, government, and the international community must act collectively to adopt the necessary protections. Walsh expressed concern that the recent spate of hacks may just be the start of more audacious attacks as hackers refine their skills.