When you think of someone leading an international ransomware operation, a teenager likely isn’t the first image that comes to mind. However, investigators have identified a 16-year-old as the suspected key operator of KillSec, a cybercriminal collective responsible for about 1,000 alleged attacks globally, with roughly 500 recognized as successful.
Recently, a coordinated international law enforcement initiative took down KillSec’s leak site and critical servers. Authorities also secured around 110 terabytes of stolen data, which could have been used to coerce victims. This crackdown highlights how accessible cybercrime has become and reveals that attackers continue to exploit inadequately protected systems to leverage stolen files for their gain. The details uncovered about KillSec showcase their operations, the role of AI, and suggest ways to mitigate the risk of ransomware attacks.
Police take down KillSec ransomware operation
The operation, dubbed Operation KillSwitch, occurred on September 30, involving cooperation between law enforcement from the U.S. and multiple European countries, facilitated by Europol and Eurojust.
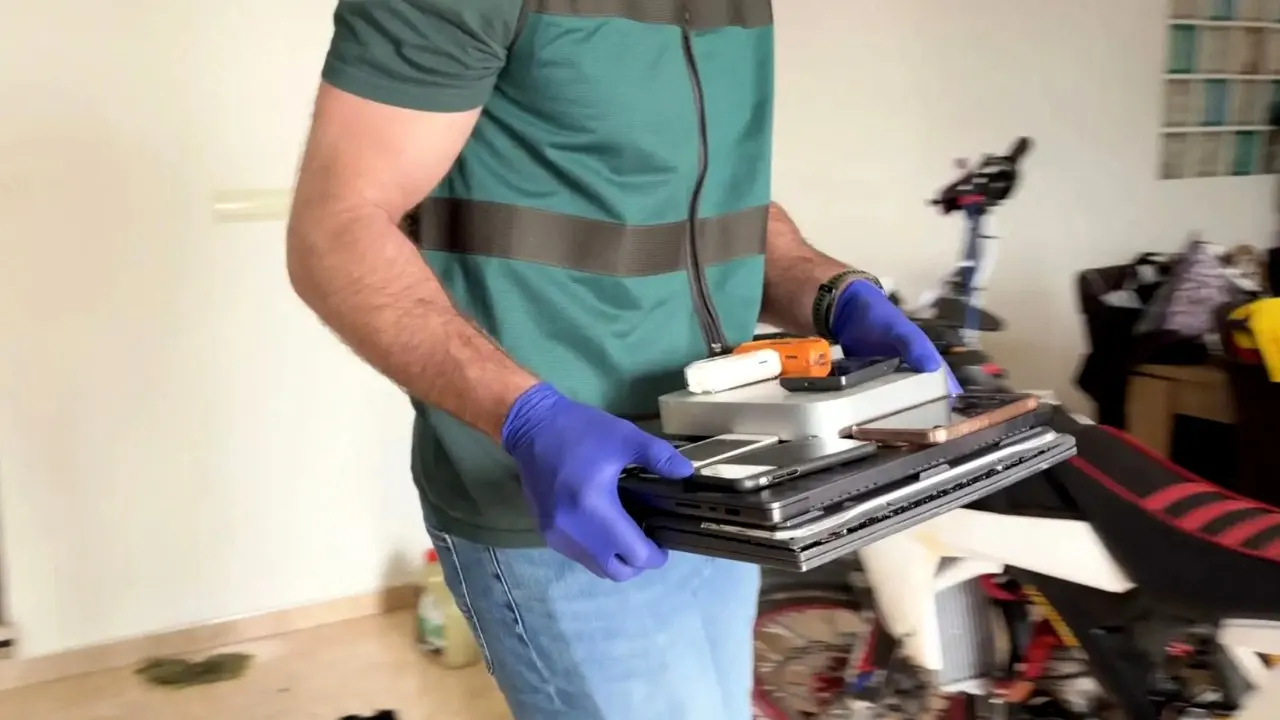
Authorities executed eight search warrants across Greece, Romania, Spain, and the UK, resulting in the provisional arrest of three suspects. They also seized five critical servers associated with KillSec’s activities. A significant portion of the operation focused on the group’s leak site on the dark web, which they used to identify victims and threaten them with the publication of stolen files unless ransoms were paid. Law enforcement has since taken control of this infrastructure.
A 16-year-old is suspected of running the operation
It’s perhaps surprising to learn that the person believed to be leading this operation is just 16 years old. Investigators have targeted this teenager as the main operator of KillSec, while another suspect, described as a developer, turned 18 recently and was likely still a minor during some incidents. There are also individuals identified as negotiators and affiliates participating in the group. Notably, KillSec, active since about 2024, is said to have exploited software vulnerabilities and poorly secured entry points to infiltrate organizations, copying sensitive files to their own systems.
How KillSec allegedly pressured its victims
Once they had the files, the pressure tactics began. KillSec allegedly named organizations on its dark web site, threatening to release data if ransoms weren’t paid. In some instances, stolen files were made public after victims refused to comply with ransom demands.
Europol indicates that the gang received significant ransom funds from various attacks. This approach shows how the nature of ransomware has evolved; attackers don’t always need to lock files to exert pressure. Simply obtaining sensitive information, such as employee records or sensitive business documents, can inflict serious damage, even if backups are available.
KillSec reportedly used AI to support its attacks
Another interesting aspect uncovered by investigators is that KillSec allegedly utilized artificial intelligence to develop and maintain their ransomware operations and identify potential targets. While AI didn’t single-handedly execute the attacks, it illustrates how cybercriminals are leveraging advanced technology to streamline their activities. In this context, it’s a reminder for everyone to focus more on their basic security practices.
What happens to KillSec now?
The investigation remains ongoing, with authorities probing seized computers, servers, and other evidence. They are also tracking cryptocurrency and other suspected criminal gains. This could reveal further attacks or connections to the operation. Europol warns that the current number of successful attacks might change as assessments of the seized data continue.
While KillSec’s foundational structure has taken a significant blow, history shows that ransomware groups often reappear under new names. Therefore, it’s crucial to maintain preventative measures even after substantial takedowns.
Why this ransomware takedown should get your attention
Although KillSec seemed to target organizations rather than individual users, the methodologies behind their attacks impart valuable lessons. Europol noted the group’s exploitation of software vulnerabilities and poorly secured access points—these are the same issues highlighted by security experts repeatedly.
Even something like an outdated router or an unmonitored account can serve as a gateway for attackers. Compromised passwords can also pose risks. Once criminals gain access, they can extract data without raising alarms. So, even if you can’t stop a global ransomware collective, you can certainly fortify your devices and accounts against unauthorized access.
7 ways to reduce your ransomware risk
A few straightforward security practices can eliminate some common vulnerabilities.
1) Install software and security updates
Stop delaying those updates on your computers and phones. Security patches often address vulnerabilities that are already known to attackers. Regularly update operating systems and software—especially on devices connected to the internet.
2) Use strong, unique passwords
Using the same password across multiple accounts can give attackers ample opportunity if one gets exposed. Create distinct passwords for important accounts. A password manager can aid in generating and storing these credentials securely. Also, check if your existing passwords have been compromised.
3) Turn on two-factor authentication
When your account requires an additional verification method, a stolen password becomes less effective. Enable two-factor or multifactor authentication on all important accounts whenever possible, opting for more secure methods like passkeys.
4) Keep an offline backup of important files
Ransomware can be particularly problematic if your only copies of files are on an infected device. Make regular backups of important documents, possibly storing one set in the cloud and another on an external drive. Remember to disconnect the external drive after the backup process.
5) Be careful with unexpected downloads and attachments
A convincing email or an unexpected prompt can be a vector for attackers. Avoid opening unanticipated files, and seek updates directly through the application rather than clicking on links.
6) Use security software on your devices
Having a good antivirus program can help detect ransomware and malicious downloads before they can do harm. Make sure it’s regularly updated, and run scans if your device starts behaving unexpectedly.
7) Know what to do if ransomware hits
If you encounter a ransom message, disconnect that device from the network. Avoid using backup drives with the potentially infected computer until you confirm it’s clean. The FBI advises against paying ransoms since payment doesn’t guarantee recovery of your data and recommends reporting such incidents.
Kurt’s key takeaways
The youth of KillSec’s alleged operator certainly catches attention, and it’s astonishing to think a 16-year-old could lead an operation like this. What lingers in my mind, though, is the familiar nature of the vulnerabilities exploited. Outdated software and insecure access points are critical openings. This reaffirms the need to focus on basic security practices: update devices, secure accounts, and keep backups out of easy reach of potential attackers. It’s a mystery which specific security measure might prevent an attack, but it’s far better to take precautions than find out the hard way.