Officials in Colorado reported that foreign hackers gained access to the computer systems of two water utilities last month. They manipulated pumping cycles, disabled alarms, and changed equipment settings before the operators managed to regain control.
According to the office of Governor Jared Polis, the security breaches didn’t compromise the quality of drinking water or its treatment processes. Nonetheless, these incidents contribute to a growing list of cyber threats targeting water and wastewater systems in the U.S.
This year alone, the Environmental Protection Agency has noted that high-profile cyberattacks have impacted over 100 drinking water and wastewater systems across 12 states. These developments have raised alarm as federal officials warned earlier this summer that such cyber intrusions are disrupting water operations nationwide.
Officials in Colorado have yet to identify the perpetrators behind these intrusions or whether they are linked to similar incidents reported elsewhere in the country. “These were short-lived events, and the risks were promptly addressed by the providers, who then informed the state,” stated Eric Maruyama, a spokesperson for Governor Polis.
The hackers changed equipment settings, shut down remote access and alarms, and adjusted pumping cycles. This highlights a worrying trend where hackers reach beyond conventional networks to infiltrate operational technology that oversees physical equipment in water treatment facilities—including pumps and valves.
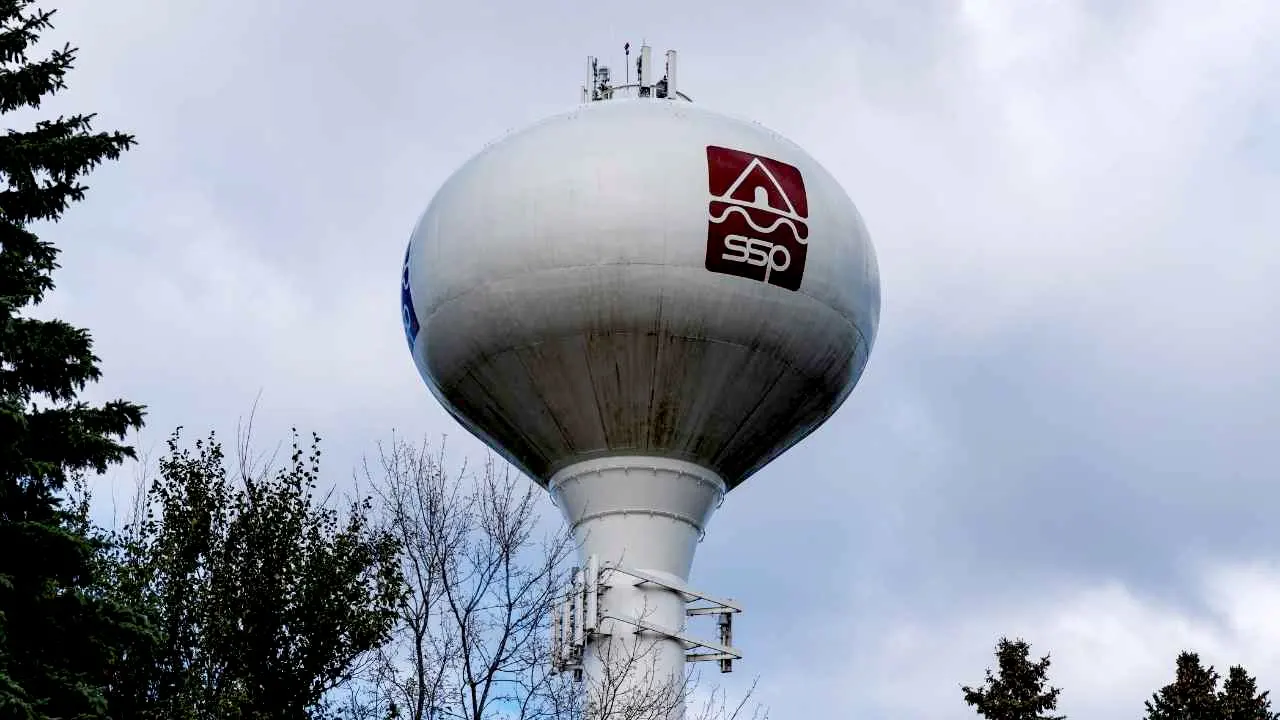
The water utility systems affected serve around 400 people. Federal authorities had previously warned that malicious cyber actors focused on internet-connected operational technology at water facilities. In July, the FBI and EPA reported incidents affecting utilities in at least seven states, some leading to deteriorated operations.
Reportedly, attackers accessed internet-facing programmable logic controllers (PLCs) and altered configurations, resulting in utilities losing their monitoring or control capabilities. This situation has led to operational issues, such as reduced water pressure and even flooding.
The breaches in Colorado come after a series of cyberattacks on water systems across the U.S. this summer, including attacks on more than 30 community water systems in Minnesota. Federal investigators have looked into whether these attacks might have connections to Iranian hackers, though there hasn’t been a public attribution as of yet.
Interestingly, during a Cabinet meeting, President Trump dismissed claims linking Iran to the Minnesota cyber incidents, suggesting instead that local officials should be held accountable.
The recent breaches have sparked renewed interest in the longstanding vulnerabilities related to cybersecurity in America’s water infrastructure, especially in smaller, rural utilities that may lack sufficient resources and skilled personnel.
A significant number of utilities utilize internet-connected industrial control systems for remote operations like monitoring pumps and valves. Federal agencies have recommended that utilities eliminate direct internet access to these programmable logic controllers and enhance authentication and access control measures.
The EPA, which serves as the federal government’s risk management agency for water systems, indicated that it is collaborating with utilities, states, and federal partners to identify vulnerabilities and bolster cybersecurity. Since the start of fiscal year 2025, the EPA has recognized over 900 vulnerabilities across more than 650 water systems and has assisted in resolving about 700 issues in over 500 utilities. They have also performed more than 710 cybersecurity risk assessments and provided direct support to roughly 15,900 utilities.
The FBI did not comment when approached regarding the situation.