Cyberattacks Target South Korean Megachurches, Exposing Personal Data
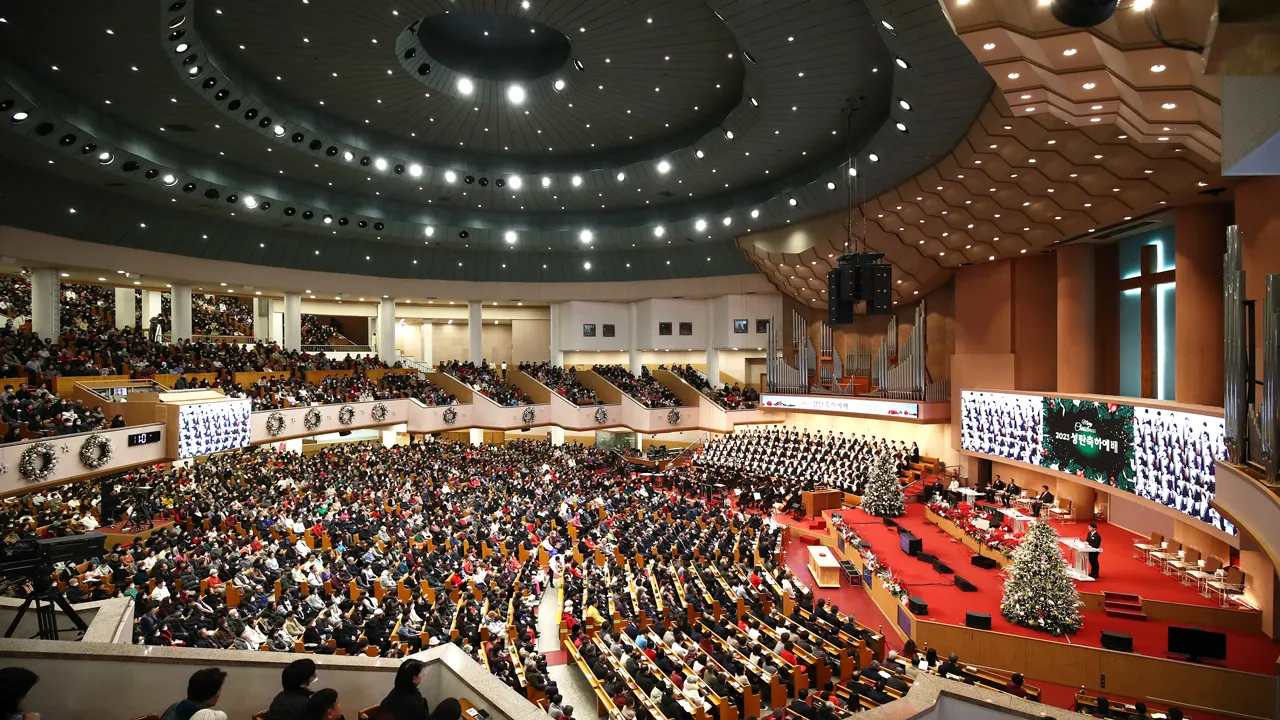
Recent suspected cyberattacks on two prominent South Korean megachurches have potentially compromised the personal data of hundreds of thousands of individuals. The Yoido Full Gospel Church and Sarang Church in Seoul are currently investigating these incidents.
Oasis Security, a cybersecurity firm, reported that it found attack logs and account details on a server located overseas, which were related to the two churches. Interestingly, indications suggest that artificial intelligence (AI) tools might have been employed during these cyber intrusions.
In a statement on Wednesday, Yoido Full Gospel Church revealed that an initial assessment suggests that data belonging to about 850,000 of its members might have been breached. This compromised information likely includes names, dates of birth, as well as a smaller amount of sensitive data, such as national identification numbers, addresses, and phone numbers. The church is in the process of notifying affected members and has also blocked external access, resetting its server passwords as a precautionary measure.
Soon after, Sarang Church announced the establishment of an emergency task force in response to the cyberattack. They have reported the security breach to local authorities and are taking further steps to investigate the incident and prevent future occurrences.
This wave of cyber intrusions adds to a concerning trend in South Korea, which has seen similar hacking incidents target commercial banks, leading to the exposure of sensitive customer information. President Lee Jae Myung noted on Tuesday that there are now signs indicating the use of AI in various recent hacking efforts involving financial institutions.