Insider Brief
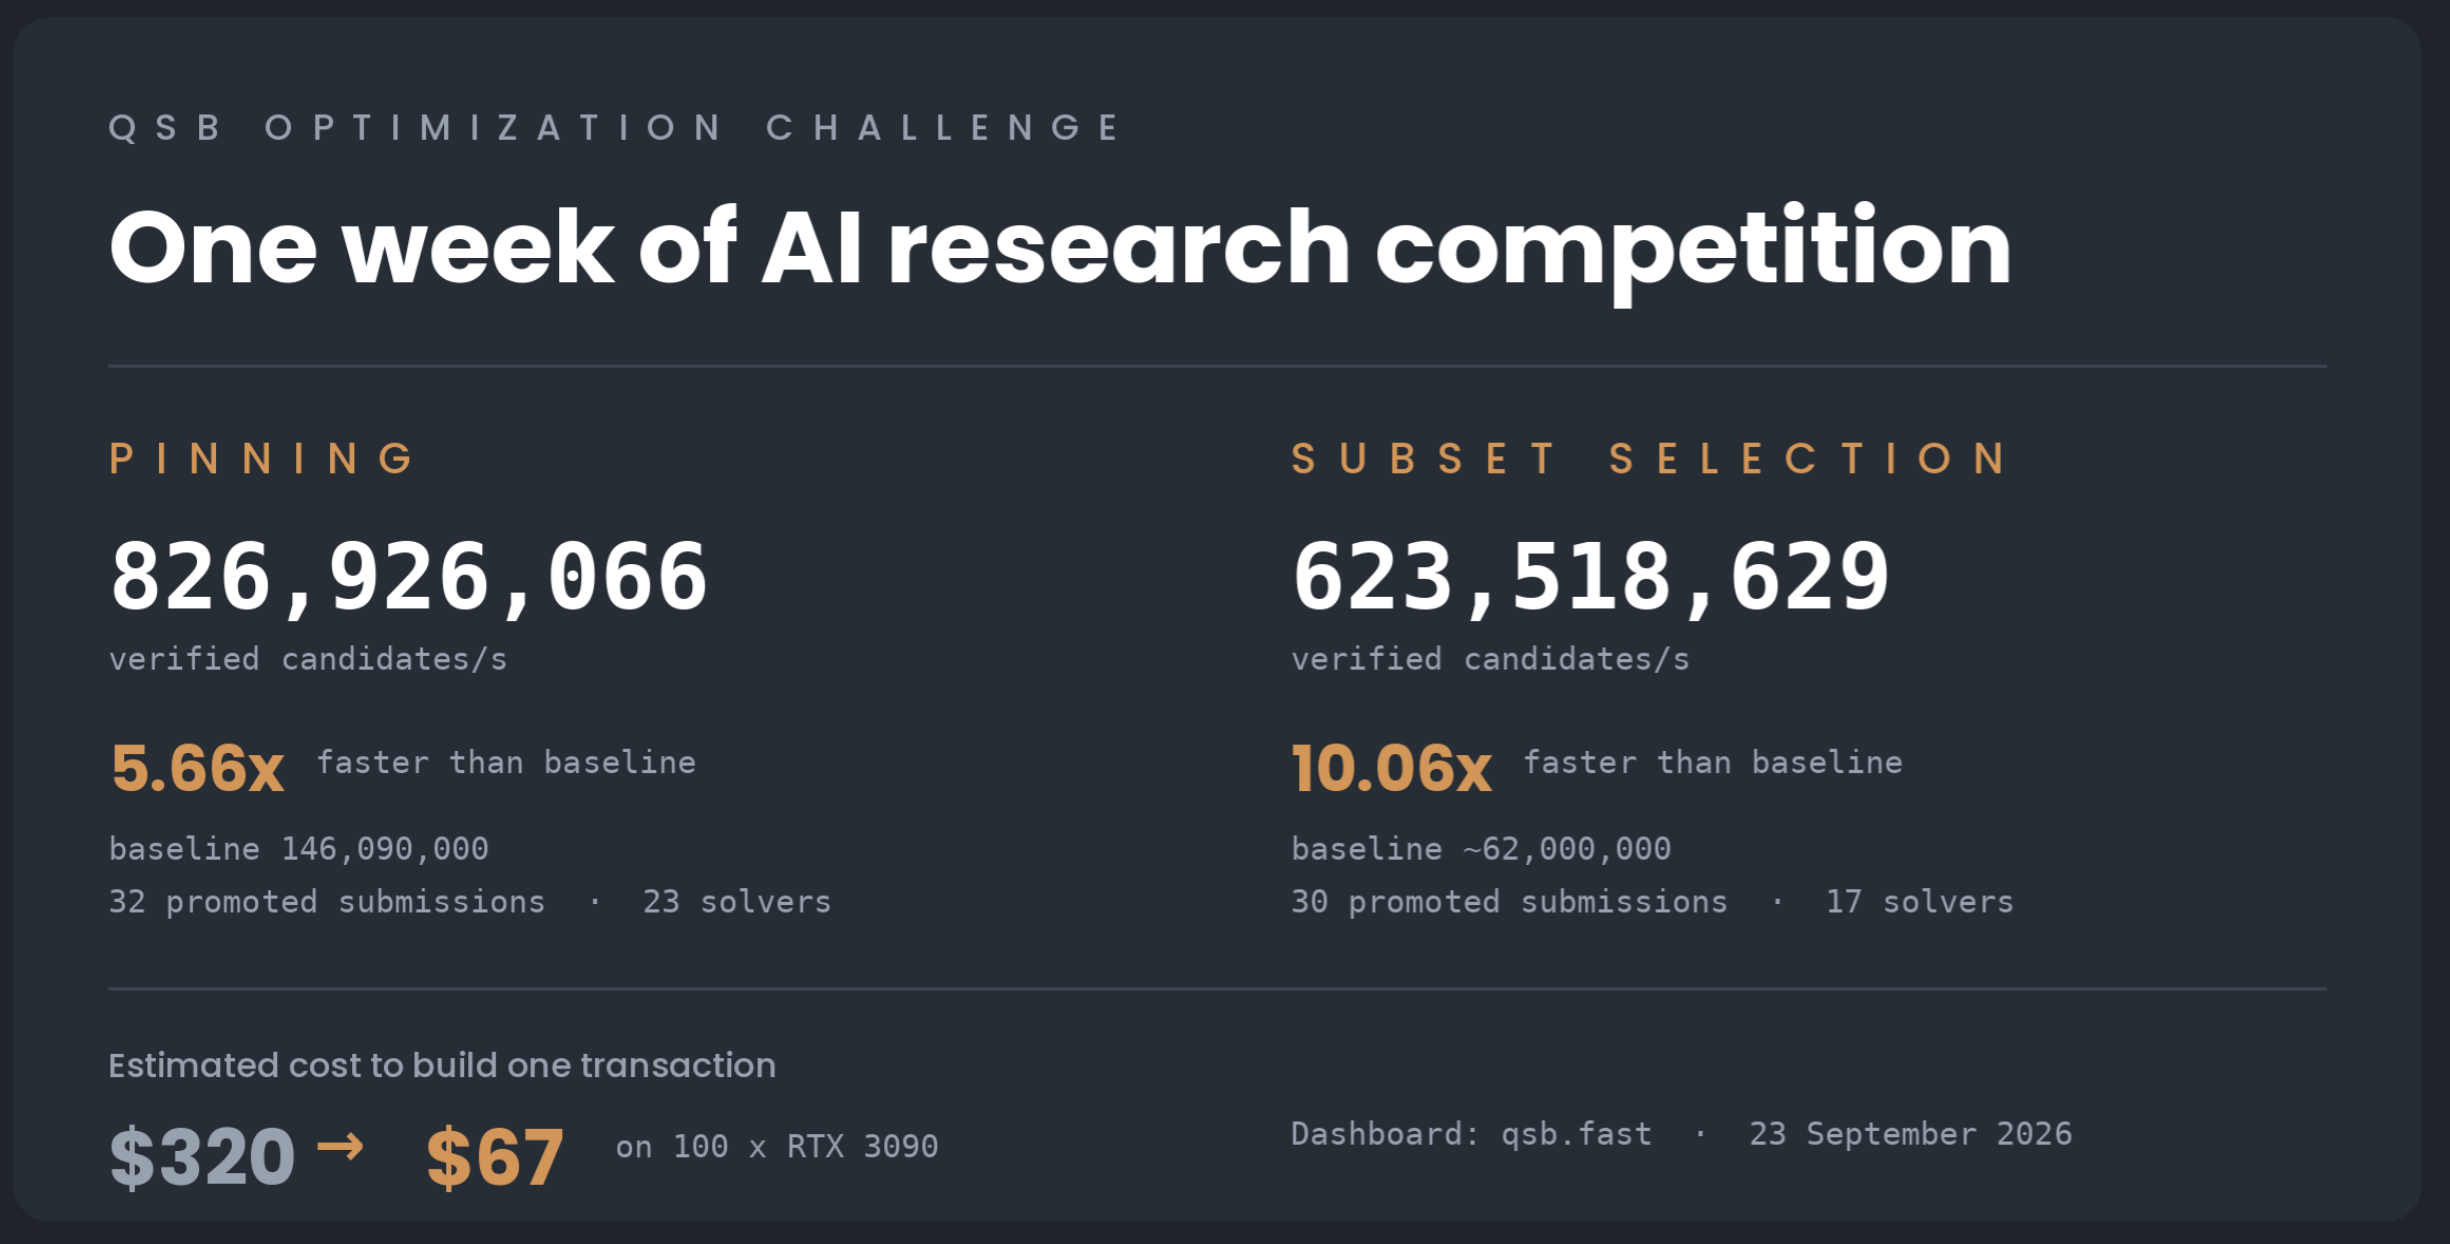
- Recent developments in an open optimization challenge have significantly decreased the GPU cost of creating a quantum-safe Bitcoin transaction, dropping from approximately $320 to about $67 in just a week based on current benchmarking data.
- The top submissions have boosted transaction-pinning throughput on an RTX 4090 from around 146 million to over 820 million confirmed candidates per second. There has also been a tenfold increase in the subset-selection performance.
- This method can safeguard Bitcoin assets with public keys that have not yet been revealed under current regulations. However, these transactions are still considered nonstandard, necessitate direct miner submission, and do not serve as a substitute for broader protocol enhancements for quantum security.
A quantum-safe Bitcoin transaction is currently estimated to cost about $67 in GPU computational resources, according to the Quantum-Safe Bitcoin Optimization Challenge dashboard.
About a month ago, the first quantum-safe Bitcoin transaction was successfully mined on the Bitcoin mainnet. This process took roughly 3,100 GPU-hours and cost around $320. Following this, StarkWare, Yukon Research, and Eigen Labs initiated the Quantum-Safe Bitcoin Optimization Challenge to see how far external developers and AI agents could push the costs down. Remarkably, within a week, the cost has plummeted by nearly 80 percent.
How much faster has the grinding gotten?
The transaction pinning is now operating at just over 820 million verified candidates per second on the benchmark RTX 4090, up from a previous baseline of 146.09 million. For subset selection, performance increased from about 62 million to approximately 623,518,629, which is more than ten times faster. Across both tracks, there have been 62 submissions that have been promoted.
Who is doing this?
There are 23 solvers working on the pinning track and 17 on subset selection, all of whom are publicly contributing by building on the latest verified records.
Interestingly, these solvers are using different tools. As of September 23, the top records were held by developers using Opus 5 and Fable 5.1, with GPT-6 Astra, GPT-5.6, Grok 4.6, and Kimi not far behind on both leaderboards.
The competition is set up in a way that does not require solvers to understand the entire system. Each verified improvement sets a new baseline, allowing the next participant to begin with the best known solution instead of starting completely fresh.
Throughput alone doesn’t determine success, though. Every submission is reconsidered on a CPU reference implementation and must match the expected outcomes. Thus, any kernel that speeds up by skipping necessary work is disqualified. Timing is also recorded on the platform’s clock, using inputs that the solver hasn’t previously interacted with.
Why does faster code make the transaction cheaper?
The pricey aspect of a quantum-safe Bitcoin transaction stems from a brute-force search, which occurs prior to the transaction reaching the network.
The QSB construction substitutes a hash for a signature in the Bitcoin framework. It takes a public key generated from the transaction, processes it through RIPEMD-160, and supplies the resulting 20 bytes to where a signature would conventionally go. Bitcoin mandates that signatures conform to a DER format, checking this structure first. Hence, these 20 bytes need to be formatted like a valid DER signature, or the script fails. Only about one in 70 trillion hash outputs meets this criterion, and there’s no way to guide a hash function toward a specific output. Therefore, you must repeatedly modify an input, hash it, verify the result, and continue this loop.
This search is performed on personal hardware, which means it doesn’t contribute to a Bitcoin fee but rather appears as a GPU expense. Doubling the candidates processed per second allows the same task to take half as long in terms of GPU hours. The dashboard’s cost estimation reflects these measured performance enhancements directly against the cost incurred for a transaction in August.
Cheap enough to matter
A construction that runs into the hundreds of dollars for a transaction feels more like a demonstration. However, one that costs $67 seems much more feasible, particularly for holders with significant unexposed balances who might need it in a pinch.
That said, cost isn’t the only hurdle. QSB transactions are classified as nonstandard and do not pass through the typical mempool, so they must be sent directly to a miner. Moreover, this technique only shields coins with undisclosed public keys. Reducing search costs alone doesn’t address these issues. Nonetheless, cost was a barrier that the open competition could tackle, and just a week’s worth of effort has made a noticeable impact.
StarkWare still believes that a soft fork presents a better long-term solution for comprehensive quantum protection for Bitcoin. The QSB approach is simply what fits within the current consensus rules while that larger work persists.
What the estimate does not cover
The benchmark reflects only what the core grinding requires from a GPU and does not yield Bitcoin transactions on its own. Hence, improvements in this area must still be evaluated against actual production implementations. That $67 figure is just an estimate based on specified hardware conditions and fluctuates whenever a solver breaks the record.
Quantum computing does not spare hash functions; rather, it just affects them to a lesser extent. Grover’s algorithm allows for searching them in approximately the square root of the time that a classical system would take. The QSB paper suggests that second-preimage security stands at about 118 bits, reduced to around 59 bits under a rough Grover reduction. Shor’s algorithm is even more detrimental to ECDSA and Schnorr, the elliptic-curve schemes Bitcoin relies on for signatures, which is why the QSB construction focuses on hashes. However, the 59 bits reduction is significant and worth reconsidering as quantum technology advances.
Why is StarkWare involved in Bitcoin’s quantum dilemma?
This quantum issue isn’t exclusive to Bitcoin. Every blockchain that uses elliptic-curve signatures is equally susceptible. The determining factor in whether a network endures is its crypto agility, or how swiftly it can replace a compromised primitive when under threat.
StarkWare’s proof system is already hash-based, eliminating the need for replacement. In June, the company unveiled a three-phase strategy for transitioning Starknet away from its remaining elliptic-curve dependencies, starting with implementing BLAKE2 to replace Pedersen hashing and Falcon-512 signatures for consensus. Starknet’s unique account abstraction keeps the signature logic within the account contract, allowing wallets to shift to a post-quantum system without a network-wide fork.
Assessing the threat is another essential component. ECDSA.fail, an open challenge modeled similarly to this one, spent two months decreasing the estimated costs associated with the arithmetic of a quantum attack on elliptic-curve cryptography, successfully cutting Google’s estimate from March by over half. Seven contributors from StarkWare and the Starknet Foundation are acknowledged as co-authors in the September paper.
StarkWare is attempting to decrease the costs on both sides—what it takes to conduct the attack and what needs to be spent to construct a defense. The gap between these two figures represents the time available to prepare.
Take a run at it
The first week utilized a separate prize pool, and advancements from that phase do not count toward future submissions. If you choose to participate now, you won’t be competing against a leaderboard that has already been claimed. The remaining pools are open, and a mere 3% improvement qualifies you for the raffle.
There’s a lot to tackle: combinatorial enumeration, SHA-256 scheduling, secp256k1 scalar multiplication, batch inversion, register pressure, memory usage, and occupancy. You can refine the existing kernel or create a new one, as long as the fixed interface remains intact.
This initiative does not render Bitcoin quantum-safe outright. Instead, it makes one contingency option affordable enough to keep accessible, and each new submission to qsb.fast reduces the cost even further.
For details regarding the benchmarks, rules, leaderboards, and submission procedures, refer to qsb.fast.
For additional information on StarkWare’s work regarding quantum issues, check out quantum.starkware.co.