Some cyberattacks kick off with a dubious email, while others might originate from sources you wouldn’t typically consider—like an old home router or an outdated security camera still linked to the internet. Hackers can exploit these vulnerable connected gadgets, masking the true source of an attack.
This approach was evident in a hacking campaign tied to China, which U.S. authorities claim targeted some of the country’s most sensitive networks.
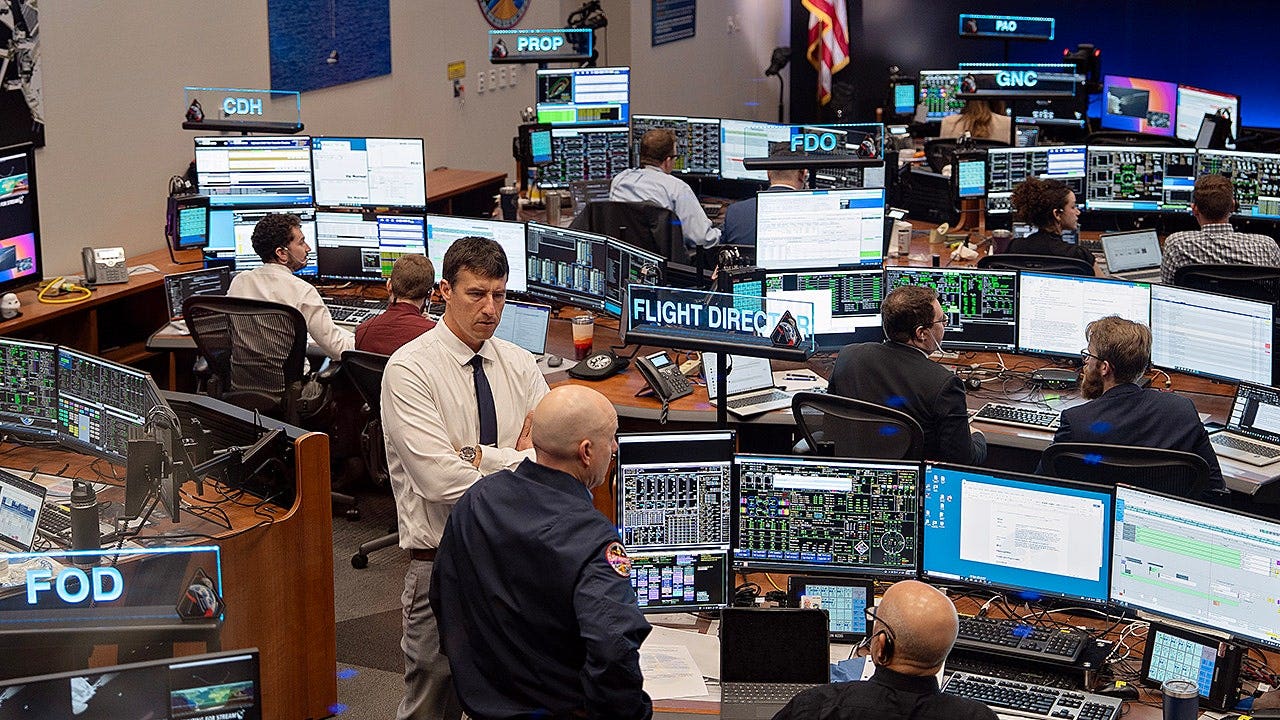
On August 26, the Justice Department and FBI revealed that intrusion attempts had been ongoing since 2018, impacting organizations such as NASA, the Federal Reserve, the Justice Department, and the U.S. Senate. Other victims included the Department of Energy, the Department of Health and Human Services, and the National Institutes of Health.
Additionally, four unspecified companies in the U.S. and South Korea were allegedly targeted. The operation behind this was associated with tools named QScan and QTRouter, which sound like they were pulled straight from an IT department, but their function is concerning.
Let’s explore how this hacking scheme operated, how it was dismantled, and some steps you can take to secure your own connected devices from becoming part of someone else’s attack network.
Chinese hackers breached NASA and other US targets
The Justice Department identifies a Chinese state-sponsored group known as QTFY as the creator of QScan and QTRouter. Officials believe the group operated for a company called Nanjing Xinjiuwei Network Technology in China, which allegedly provided hacking tools to clients, including the Chinese Ministry of State Security and the People’s Liberation Army.
Authorities report that the QTFY infrastructure has been at work since at least 2018, compromising critical infrastructure and sensitive networks. Legal documents detail that targets also included hospitals, telecommunications services, financial institutions, and defense contractors.
We reached out to NASA for comment regarding the Justice Department’s announcements.
“NASA is dedicated to cybersecurity and the safeguarding of our systems,” said NASA spokesperson Jennifer Dooren. “We collaborate closely with federal partners to promptly address any vulnerabilities we discover. Our efforts to monitor, assess, and protect our software and networks are continuous.”
She added, “For security reasons, we do not discuss specific incidents or vulnerabilities. For more details, please direct inquiries to the Department of Justice.”
The Chinese Embassy in Washington was also contacted about this situation.
“I’m unaware of the specifics you’re mentioning,” a spokesperson responded. “China staunchly defends cybersecurity and opposes all forms of cyberattacks in accordance with the law. We urge the U.S. to refrain from using cybersecurity issues to defame or discredit China.”
The embassy added that China is against the U.S. broadening the concept of national security to impose restrictions on Chinese businesses, asserting that it will protect their legitimate rights and interests.
After being sent the Justice Department’s statement detailing the QScan and QTRouter allegations, the embassy had “no further comments at the moment.”
China has refuted claims about its involvement in malicious cyber activities. What’s notable is the infrastructure utilized in these attacks. Investigators describe a system designed to locate vulnerable devices, which were then used to obscure malicious endeavors.
How QScan and QTRouter worked
QScan was responsible for identifying vulnerable systems, automatically compromising thousands of internet-connected devices globally. These infected devices were then integrated into QTRouter.
QTRouter was described as an obfuscation network, meaning it concealed the origin of the attacks. This system comprised compromised IoT devices along with commercial proxies and rented virtual private servers.
Attackers could funnel harmful communications through this infrastructure, making it appear as though the activity was coming from outside of China or from the vicinity of the targeted network. This presents a significant challenge for security teams trying to trace the source of an attack.
Consider all the internet-connected equipment that often goes unnoticed after setup. A router perhaps sits untouched for years, while a security camera might remain operational long after updates are no longer provided. It’s these neglected devices that hackers target, using them as a hiding place.
FBI Director Kash Patel highlighted the role of this infrastructure in obscuring the attackers’ identity.
“These tools were utilized by Chinese cyber actors to disguise the origins of their attacks,” he stated.
Why your connected devices enter the picture
You were likely not on the hackers’ radar. NASA and the Federal Reserve operate under very different security protocols than those in your home. Nonetheless, the underlying infrastructure of these attacks links back to everyday technology.
QScan allegedly infected IoT devices, pulling them into a larger network, which then camouflaged malicious traffic. So, an insecure device can become a valuable asset to an attacker, even if they have no particular interest in its owner.
There’s a chance you might never see a ransom demand. Your smart device could work fine on the surface. However, vulnerable devices can facilitate malicious activities occurring elsewhere. That’s why I constantly stress the importance of checking the router collecting dust behind your couch.
How federal agents pulled the plug
The Justice Department secured court approval to seize domains related to QScan and QTRouter, which turned out to be a critical vulnerability. These domains were hard-coded into the malware, serving essential functions like communication and authentication. Once they were seized, the Justice Department reported that the malware platforms became nonfunctional. Authorities effectively targeted the infrastructure that these hacking applications relied upon.
According to Black Lotus Labs, addressing shared infrastructure can dismantle multiple cyber operations at once. Their research indicated that “taking down a single quartermaster’s obfuscation network systematically undermines the capabilities of various active threat campaigns at once.”
Black Lotus Labs also noted that they shared intelligence with U.S. government agencies regarding emerging threats and redirected traffic away from known infrastructure used by the operators. They characterized the operation as a form of cyber “quartermaster,” providing reconnaissance, routing, and concealment capabilities leveraged by multiple China-linked threat actors. This strategy has increasingly been part of the U.S. response to China-related cyber threats.
This follows years of China-linked hacking warnings
This recent operation builds on prior federal initiatives aimed at Chinese hacking groups. In 2025, the FBI eliminated PlugX malware from over 4,000 U.S. computers linked to the Mustang Panda group. The previous year, federal agents took down a botnet composed of hundreds of thousands of infected IoT devices associated with Flax Typhoon.
The FBI also disrupted another botnet employed by Volt Typhoon to conceal attacks directed at U.S. and global critical infrastructure. CyberGuy has also covered Salt Typhoon, the China-associated hacking campaign that infiltrated significant American telecommunications networks. Each operation has its unique method, but they all illustrate the value of compromised infrastructure to state-sponsored hackers.
How to protect your router and connected devices
While you can’t halt a state-sponsored cyber operation by yourself, you can take steps to make it significantly harder for attackers to compromise your devices or utilize them as part of their infrastructure.
1) Update your router firmware
Firmware is the software that runs on your router, and security fixes are often sent out via firmware updates. Make sure to log into your router’s app or admin page and look for updates. If possible, enable automatic updates.
2) Replace outdated routers
Old routers may remain operational long after their manufacturers stop providing security updates. Check the model number on the manufacturer’s website to see if it still receives updates. If it’s outdated, you should consider a replacement. The FBI has cautioned against using aging routers that lack security patches.
3) Change the admin password
Don’t keep the default administrator password for your router. Create a long and unique password that you’ve never used elsewhere. A password manager can help. If your router offers two-factor authentication, activate it.
4) Use a robust Wi-Fi password
Your Wi-Fi network must have its own secure and unique password. Avoid using easily guessable personal information. Make sure this password differs from your router admin password.
5) Opt for WPA3 encryption if possible
Review your router’s wireless security settings. WPA3-Personal offers enhanced protection and should be your go-to option if all your devices support it. If it causes compatibility problems, use WPA2-Personal with AES or a mode that supports both WPA2 and WPA3. Steer clear of older WEP and WPA protocols.
6) Disable remote admin access
Most users don’t need to change router settings while away from home. Look for a setting called Remote Management or Remote Administration and turn it off unless absolutely necessary. The FBI has emphasized that exposed remote administration can give attackers another avenue to exploit vulnerable routers.
7) Disable WPS and unnecessary UPnP
Wi-Fi Protected Setup (WPS) can simplify connectivity, but it’s generally not needed after setup. Check for Universal Plug and Play (UPnP) access; disabling it when not required can reduce exposure.
8) Ensure your router’s firewall is active
Most routers come equipped with a built-in firewall. Confirm in the settings that it’s enabled. Avoid altering advanced firewall settings unless you understand their implications.
9) Put smart devices on a separate network
If your router supports guest networks or dedicated IoT networks, separate your smart devices like cameras and speakers from devices that handle sensitive information. This makes it harder for attackers to access your critical data if one device is compromised.
10) Update all connected devices
Your router is just one segment of the network. Check for software updates on other smart devices and enable automatic updates if available. If a device has reached the end of its support lifespan, consider replacing it.
11) Change default passwords on IoT devices
Devices like cameras often come with preset passwords; change these during setup. Use distinct passwords for each device to increase security.
12) Review your Wi-Fi connections
Regularly check your router’s app or admin page to see all connected devices. If you find any unrecognized devices, investigate further. Change your Wi-Fi password if needed.
13) Disconnect unused devices
Old hardware like cameras or smart plugs may still be connected to your network. Remove any devices you no longer use, resetting them before disposal.
14) Keep your computers and phones updated and protected
Install the latest operating system and security updates on all devices. Strong antivirus software can help detect potential threats before they compromise your security.
15) Recognize signs of a compromised router
If you notice unexpected changes, unfamiliar devices, frequent connectivity issues, or odd router behavior, take action. Restart your router and check for unauthorized settings. Persistent problems may require contacting your internet service provider or even resetting the router.
Kurt’s key takeaways
It’s hard not to notice the lengths taken to hide the origins of these attacks. The hackers seemingly created infrastructure to identify and exploit vulnerable devices, then used those devices for cover. Federal agents achieved a significant victory by seizing crucial domains required for the malware. However, it’s just one battle in a much larger cyber conflict.
State-backed groups continue their quest for vulnerable infrastructure because neglected devices are prevalent. Your router—often just a means to connect to Netflix—can have a very different use from an attacker’s perspective. So, the practical takeaway? That aging router you’ve overlooked deserves an inspection, and the same goes for any outdated smart devices still connected to your network. Are you confident in the measures taken to prevent these attacks, especially from China-backed hackers? Let us know what you think.